
Open a WhatsApp attachment and lose your entire PC, AI scams are slipping past the very security steps meant to protect you, and now even photos and videos come with “AI-generated” warnings. Here’s the news you can’t afford to miss this week.
Table of Contents
Why You’ll Soon See More ‘AI‑Generated’ Tags on Photos and Videos
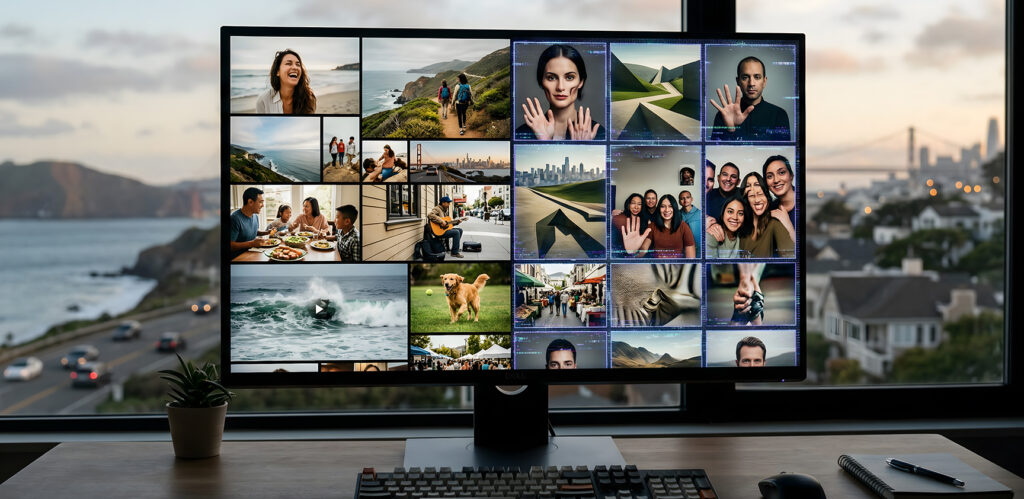
California is starting to roll out new rules requiring big tech companies to clearly mark when photos, videos, or texts were made by AI rather than a real person. The goal is to help people spot fake or edited content online, especially around elections, where AI‑generated “deepfakes” can mislead voters.
Some of the rules require AI companies to build in hidden tags that say “this was made by AI” and to give users tools to check whether a piece of content is real or synthetic. The laws are still evolving and facing legal challenges, but over the next couple of years, expect to see more “AI‑generated” labels on content from major platforms, even though bad actors and smaller tools will still try to hide what’s fake.
- If something important looks shocking, especially during an election, treat labels and fact‑checks as a first step, not the only step, and double‑check with trusted news sources.
- Even with new rules, scams and fakes won’t disappear, so keep your guard up: if a piece of content seems designed to make you angry, scared, or rushed, slow down before you share or act on it.
https://ai-law-center.orrick.com/california
New WhatsApp for Windows Scam Turns One Click into the Full Takeover of a Windows PC
Attackers are now sending booby-trapped attachments over WhatsApp for Windows that can quietly give them remote control of a PC if the user opens the file. The trick relies on a simple script that abuses built‑in Windows tools, so the activity doesn’t look obviously malicious. Once it’s in, the malware tries to get admin rights, weaken security prompts, and install remote‑access software so criminals can stick around and steal data.
- Be suspicious of unexpected WhatsApp desktop attachments, especially anything that isn’t a clear document or image, and double‑check with the sender before opening.
- Turn on file‑extension viewing in Windows so files ending in .vbs, .cmd, .bat, or .msi jump out as high‑risk, and run up‑to‑date security software that can spot script abuse.
- Use a standard (non‑admin) Windows account for daily work and treat any surprise prompt to “allow changes” right after opening a chat attachment as a stop sign, not something to click through.
Face ID, Not Texts: The Better Way to Safeguard Logging in to Your Accounts
We’ve been telling users to move to multi-factor authentication whenever possible. Now we need to get more specific. Criminals are getting very good at tricking people into reading those codes out loud, or at quietly taking over phone numbers so the codes go straight to them instead of you.
Once they have your password and that one-time code, they can drain accounts or lock you out in seconds. Now, users just need to switch to stronger options that are built into the devices and apps they already use.
- Turn on biometric login (Face ID, Touch ID, fingerprint, or device PIN) for your banking app, password manager, and email whenever it’s offered as an alternative to those SMS codes.
- Use a password manager to create and store long, unique passwords for every account, and then protect that manager with your device’s biometric login.
- In security settings, switch from text-message codes to an approval inside your bank app.
- Never read a code to anyone who contacts you and never type a code into a site you reached by clicking a link in a text or email.
Home Wi-Fi Router Ban is Underway: Software Updates End March 1, 2027
In the U.S., security updates for foreign‑made home routers will be allowed until March 1, 2027, under a blanket FCC waiver, but no new foreign‑manufactured consumer router models can be approved for sale in the US going forward. Data from Ookla show that the hardest‑hit brands will include TP‑Link, along with contract manufacturers Arcadyan and Askey, which build gateways for Verizon and Charter, because their hardware is overwhelmingly manufactured in China and Taiwan.
By contrast, US‑based brands that can shift assembly or qualify for exemptions, such as Netgear and Amazon‑owned Eero, may have more room to adapt, though they also rely heavily on overseas supply chains today. For now, consumers and organizations can keep using and even buying already‑approved foreign‑made routers; the clampdown applies to certifying future models, which is expected to shrink choices, slow Wi‑Fi 7 rollouts, and push prices higher over the next several years.
The White House defends the policy as a national‑security measure to reduce supply‑chain risk, while industry groups warn it will do more to disrupt the router market than to fix real‑world cybersecurity problems.
Lesson from an AI Company’s Accidental Leak: Employees’ ‘Helpful’ AI Assistant May Be a Powerful Tool for Hackers
Several AI companies are about to release a new wave of powerful systems capable of breaching computer networks, making large-scale cyberattacks easier to launch than ever before. An accidental leak of Anthropic’s upcoming tools shows how powerful these capabilities are and how much information its desktop assistant can quietly collect from any computer on which employees install and use it.
About half of workers now say they use AI tools at work without permission and often connect them directly to company email, files, and internal systems, greatly increasing hidden risk for the business. The takeaway is that AI assistants must now be treated like high‑risk software. Messaging to your workforce must consistently remind them that only approved tools are permitted and that employees must not enter sensitive company information into personal AI assistants.
Cambodia Finally Targets Scam Compounds Where Human Trafficking Victims Work the Phones
Many of the scam calls and messages people receive today are not coming from “willing criminals,” but from human‑trafficking victims locked in compounds and forced to defraud strangers online. Cambodia has just passed its first dedicated cybercrime law targeting these scam centers, introducing prison terms of up to 10 years and fines of up to $250,000 for gang‑run operations, along with penalties for money laundering, stealing victims’ data, and recruiting workers into the scams.
Officials say this “strict fishing net” law is meant to back a wider crackdown that has already closed hundreds of sites and follows growing international pressure.