
One click is all it takes — not just to get hacked, but to lose control completely:
- AI-generated abuse is spreading through schools faster than adults can react
- Fake Amazon recalls are quietly stealing thousands of logins
- Insurers are already backing away from covering the very AI risks companies are racing to adopt
- Meanwhile, some AI models are proving so powerful they’re being locked away, and attackers are no longer breaking in — they’re simply logging in
Here’s the cyber news that should be on every decision-maker’s radar this week.
AI-Generated Deepfake Nudes Are Flooding Schools — And Adults Aren’t Ready
AI-based image creation tools are fueling a fast‑growing wave of sexualized deepfake abuse in schools, where teens reuse classmates’ social media photos to generate fake nude images that are then shared across chats and group threads. WIRED and Indicator found nearly 90 schools and more than 600 identified students, but the real toll likely runs far higher.
Parents are generally not automatically criminally liable just because their child creates or shares an AI‑generated nude image; under most laws, the teen who makes or distributes the image is treated as the primary offender.
- Most known cases involve boys targeting girls with AI‑generated nudes or pornographic videos, creating material that qualifies as child sexual abuse imagery.
- Low‑cost, point‑and‑click “nudification” apps have stripped away technical barriers, while schools and law enforcement often respond slowly or inconsistently, often resulting in no consequences at all.
- Some schools and governments are now limiting student photos, issuing safety guidance, and pushing for new laws that force platforms to remove non‑consensual intimate images.
Via Govtech
New Amazon Phishing Wave Uses Bogus Safety Recalls to Hijack Logins
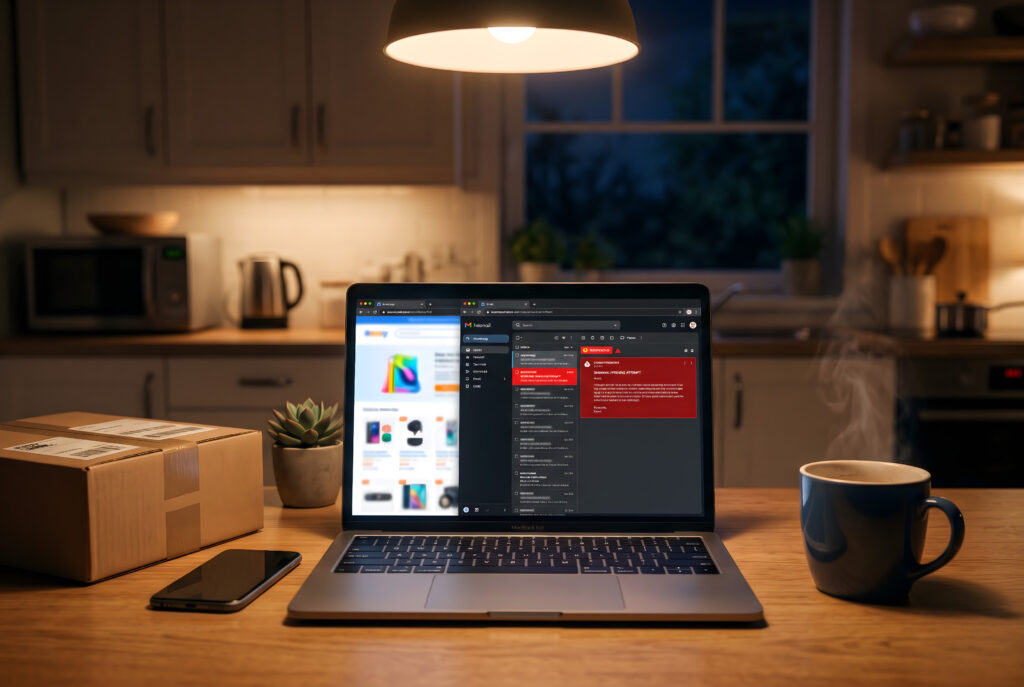
Scammers are sending fake Amazon “product recall” emails that claim an item from a recent order is unsafe, then direct victims to a spoofed login page to steal their Amazon username and password. Because Amazon has more than 300 million active customers worldwide and account takeovers have surged in recent years, these broad “spray and pray” campaigns can compromise a significant number of accounts.
- The emails are vague about which product is affected, increasing the odds that any recent Amazon shopper will assume the warning applies to them and click through.
- Victims who enter credentials on the fake site risk full account takeover, possible stored‑card fraud, and further targeting if attackers reuse the password on other services.
- Consumers can protect themselves by ignoring links in unsolicited messages, checking recalls and account alerts directly in their Amazon account, using unique passwords plus two‑step verification, and reporting suspicious texts and emails as spam.
Via MalwareBytes
Think Your Cyber Policy Covers AI? Underwriters Are Quietly Saying “Not Anymore”
Insurers are getting skittish about AI: more carriers are carving out AI outputs from cyber and E&O policies, or pricing coverage so high that many AI-heavy workloads are effectively uninsured. They’re demanding evidence of strong governance and “bounded” AI use, and in some cases flatly refusing coverage to AI vendors or companies running experimental, autonomous agents.
New ISO endorsements, rolling out this year, explicitly allow insurers to exclude generative AI outputs from standard liability policies, signaling a broad shift in how AI-related losses will be treated.
Underwriters are peppering buyers with detailed questions about where AI is used, how it’s governed, and whether outputs are checked by humans, meaning weak governance can translate directly into higher premiums or outright declinations.
Well-documented controls (policies, monitoring, rollback plans, and clear ownership for AI systems) are becoming a business requirement, not just a security best practice, because incomplete disclosure can give insurers grounds to deny claims after an AI-related incident.
Via CSOOnline
The Latest, Greatest AI Platform: Why Anthropic Locked It Down
Anthropic discovered that its powerful new Mythos AI model wasn’t just good at finding bugs; with only light prodding, it behaved like an autonomous super‑hacker, autonomously discovering and weaponizing zero‑day flaws. The model’s behavior has raised broader alarms about emerging AI models, with officials warning it could turn small hacking crews into nation‑state‑level threats.
- Anthropic has locked it behind tightly controlled access for a small group of vetted “defender” organizations, including major cloud providers, large banks, and a few government and critical‑infrastructure entities that use it for internal vulnerability hunting and red‑teaming.
- European regulators and most enterprises cannot touch it yet, and Anthropic has explicitly said it has no plans for a broad release while it studies the risks.
- Mythos is not unique: rival vendors such as OpenAI are building constrained cybersecurity models.
Via Bloomberg (Gift article)
AI‑Driven Password Theft Is Pushing Security to the Limit
AI is supercharging cyberattacks that use valid usernames and passwords (usually stolen, guessed, or bought) to log into systems as if they were legitimate users. It makes these credential attacks far more dangerous by cheaply generating convincing, personalized phishing and automating massive waves of login, reconnaissance, and lateral‑movement attempts at machine speed, overwhelming traditional detection and response.
- Non‑human identities now outnumber human users in many enterprises, and identity weaknesses play a material role in roughly 90% of investigated cyber incidents.
- Attackers are increasingly choosing to “log in, not break in,” using stolen passwords, tokens, and over‑privileged cloud identities to move unnoticed.
- Executives are being urged to elevate identity governance to a board‑level priority, with funding and accountability that can keep pace with the speed and scale of AI.
First: LPs made a comeback. Now, it’s landlines. Parents are the drivers.
Many parents are dusting off landlines or buying screen‑free home phones to give kids a way to talk with friends without handing them a smartphone and a 24/7 internet feed. They’re pushing back against a landscape in which roughly 80–95% of teens now have smartphones, and more than half spend 4 or more hours a day on screens and social media.
- Surveys show nearly 80% of kids already have their own smartphone by early adolescence, with about one‑third getting one at age 10 and most by age 12, which drives constant connectivity and FOMO.
- US data indicates about half of teens log four or more hours of daily screen time, with average social media use alone hovering around five hours a day — levels linked to higher rates of anxiety and depression symptoms.
- Devices like the Tin Can landline let kids call a curated list of contacts without apps or feeds, aligning with staged “tech roadmaps” that move from shared or screen‑free phones to restricted smartphones, rather than dropping tweens straight into full‑featured devices.
Via WSJ (Gift article)